
Financial Regulation ”“ the opportunity for FinTech Research & Innovation
The UK’s approach to financial regulation has been key in enabling a dynamic financial services sector that supports and drives the economy, enables a progressive economic outlook, creates jobs, and plays a significant role as a global financial service centre.
The development of this Roadmap highlighted financial regulation as a priority theme because of its fundamental role in FinTech and financial services, as well as the need for financial regulation to support the positive role FinTech innovation could play in the future of finance.
Regulation remains extremely complex for all those operating in the finance industry. Depending on the complexity of the financial institution’s business model, meeting compliance obligations can mean significant costs.
Industry research suggests that some of the largest global financial institutions are spending up to 5% of revenue on regulatory compliance. Across the UK this could mean the annual cost of demonstrating regulatory compliance is as much as £6.6 billion.
Throughout the development of the Roadmap, contributors highlighted their interest in the role technologies could play in future financial regulation. Some examples are AI, advanced analytics, high performance computing including quantum computing, and distributed ledger technologies.
Priority areas in Financial Regulation
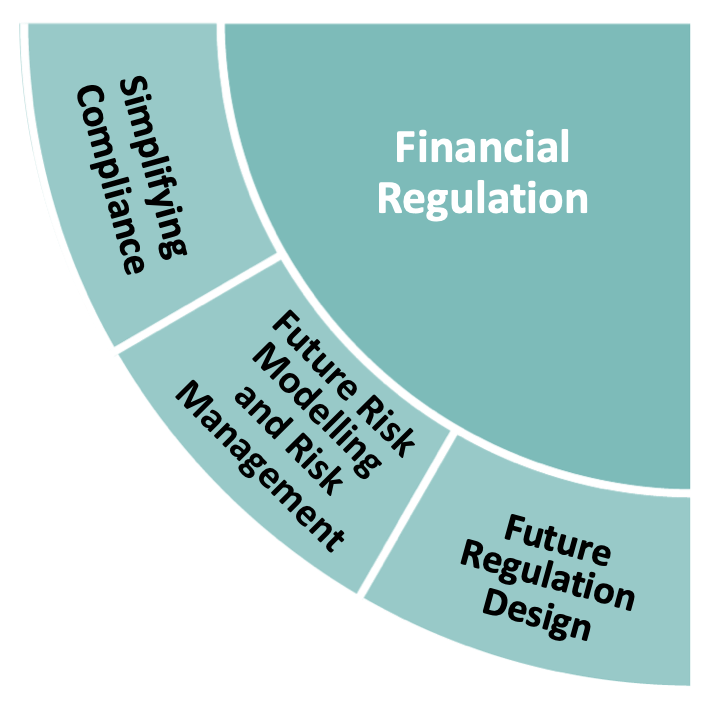
The industry contributors to this roadmap offered a view that the future looks set for significantly more change. Our analysis highlighted three topics of interest:
Simplifying compliance
Helping financial institutions create new solutions and use FinTech to help meet current, continuously changing, and global regulatory obligations.
Future risk modelling and risk management
Reinventing risk management with technology and data analytics, and enabling new approaches to fight financial crime, address fraud and focus on emerging climate risks.
- Reinventing risk management with technology and data analytics
- Enabling new approaches to address fraud and fight financial crime
- Modelling for new and emerging climate risks
Future regulation design
Enabling an agile regulatory framework that works for all, and developing future regulatory oversight or supervisory technology.
- Regulatory reporting
- Interoperability and data standardisation
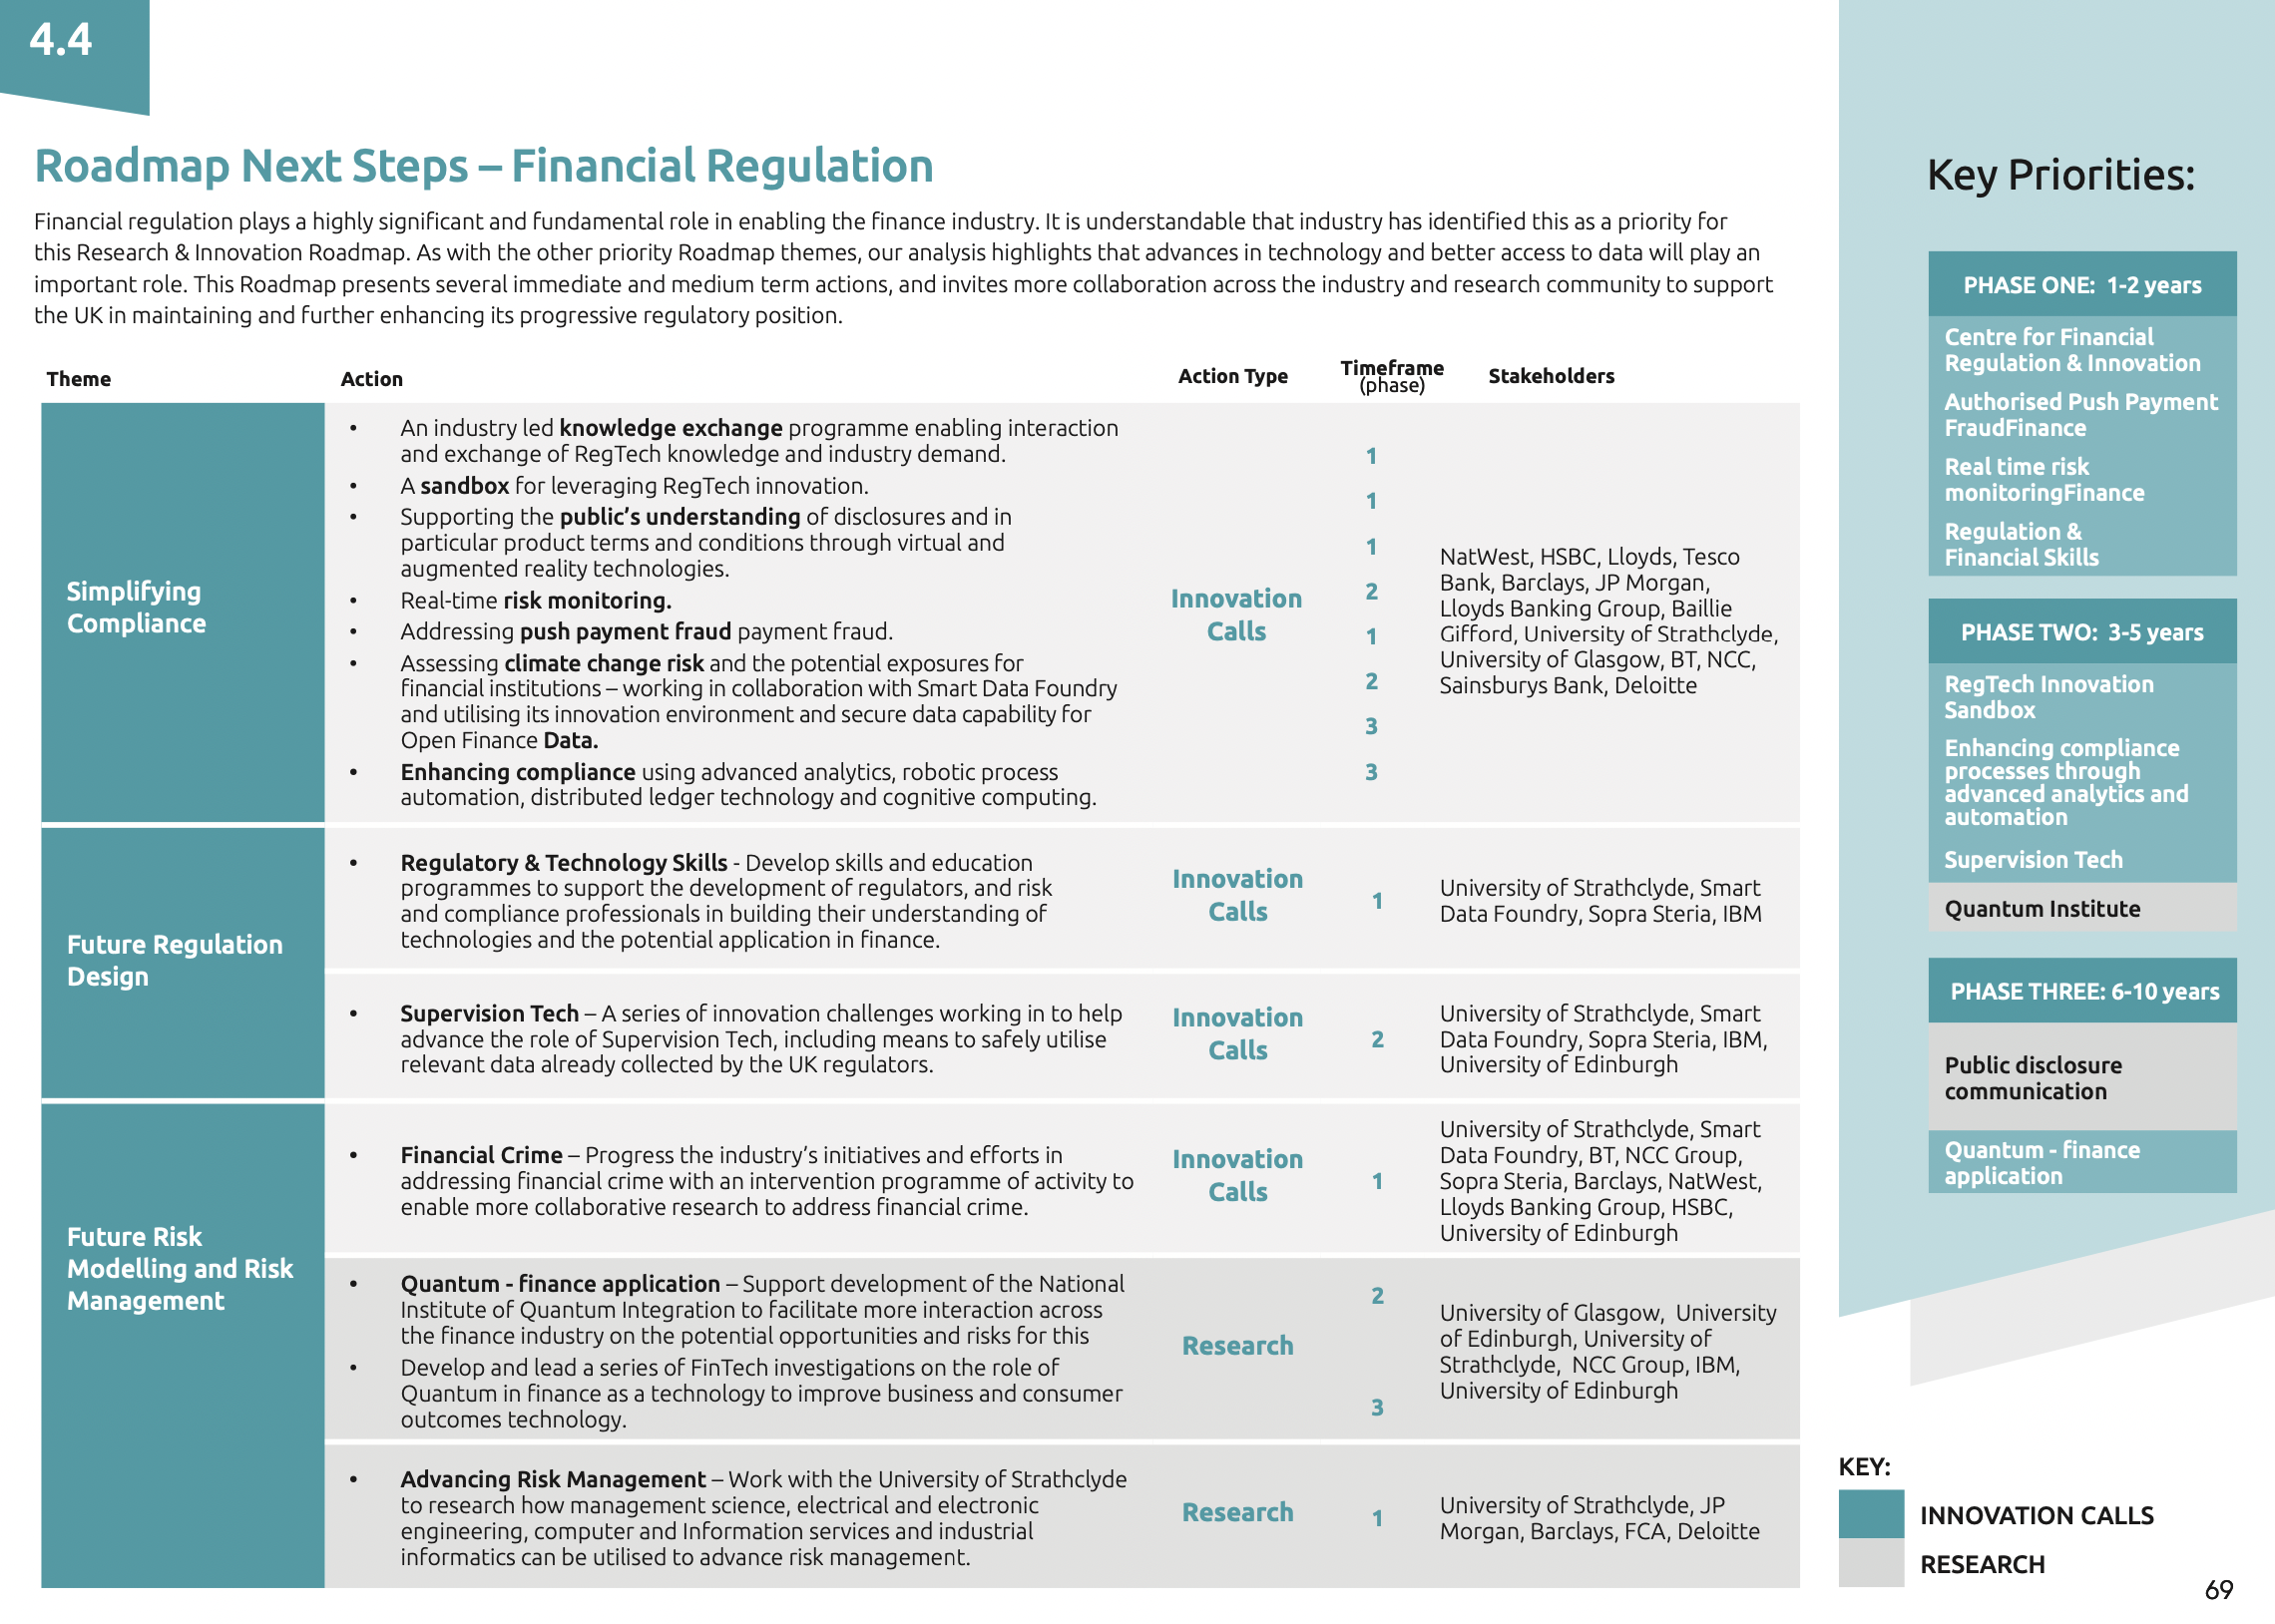
Roadmap next steps: Financial Regulation
A range of proposed next steps are laid out in the published Roadmap, which specifically identifies 13 actions relating to Financial Regulation, and categorises each into one of three phases over the next 10 years. These actions are illustrated in the graphic below. The report also references 23 different stakeholders who can support the implementation of these actions, which are broken down into research projects and innovation calls.
More information about FinTech Scotland’s Research & Innovation Roadmap can be found here, where the full Roadmap can also be downloaded.
The Identity Tooling Needed for Institutional Adoption of DeFi
Blog written by Kai Jun Eer, founder of fintech Onboard ID
In the past year, the term Web3 has become an increasingly used buzzword. The growth in different blockchain protocols and metaverse projects seem to have shed a light on how the new Web3 might look like. We are on the forefront of technology innovation, and we are really excited about it. Yet, it is important to remember that Web3 is not just about crypto and metaverse, but how we define a more user-centric internet. Behind every shining DeFi protocol or NFT project, there is an infrastructural layer supporting them.
Most of the current decentralised finance (DeFi) protocols are pseudonymous in nature (meaning each user is tied to an identifier but not to its real world identity). As these protocols start to grow into institutional adoption, inevitably they will need to comply with certain institutional regulations. One example being some of the users might now need to undergo the Know-Your-Customer (KYC) verification in order to continue interacting with these institutions through the DeFi protocols. I envision that as DeFi matures, the underlying protocol that facilitates the settlement / transactions would be fully decentralised and trustless, while specific use cases can be built on top of the protocol where some might introduce regulations.
A concrete example is Aave, one of the largest DeFi protocols deployed on multiple blockchains such as Ethereum and Avalanche. Aave first started out as a decentralised lending and borrowing protocol. Earlier this year, Aave launched a permissioned protocol (Aave Arc) that targets institutional adoption. The benefits that a blockchain can bring to speed up efficiency of financial settlements do not have to be limited to a fully decentralised setting. However, users that interact with Aave Arc have to undergo KYC in order to meet regulatory requirements.
As more DeFi protocols are becoming more regulated to expand their markets to financial institutions, does that mean that as an end user, each time I want to access a different protocol, I have to undergo a KYC verification again and again? Other than not user-friendly, it makes an already high barrier to entry in DeFi even less accessible.
A digital identity might help. Imagine if an end user only has to undergo the KYC process once, where it receives a digital identity which can be subsequently presented to the different DeFi protocols. With increasing awareness of data privacy and data ownership, users want to be in control of their own data. As an end user, I no longer want to delegate my identity data to a centralised data custodian (think Google ID), especially sensitive data such as what financial services I am accessing. There is a need for a privacy-preserving identity solution, which provides convenience yet still user-centric.
At Onboard ID, we are building the next generation identity tooling, where users are always in control of their own data. Once a user has undergone the usual KYC verification, it receives a cryptographic digital credential which contains the user’s verified identity data. The identity data is only stored in the user’s mobile phone and not in any central databases. An identifier of the credential is recorded on a public permissionless blockchain, such that when the user presents its credential, it is verifiable that the identity data in the credential comes from the trusted KYC provider. The reason our solution is user-centric is that during KYC reverification, data transfer only happens between the user and the verifier without passing through any third parties, not even us as the infrastructure provider. Therefore, users are always in control of how they want to share these data and with whom.
We are currently in beta testing. If your organisation is looking to get an edge in streamlining KYC reverifications, whether it’s in the fintech sector, looking to get into DeFi, or other more specific use cases, please get in touch at kaijuneer@gmail.com! Our vision is to contribute towards building a more user-centric internet, and we hope you could come onboard with us.
Protecting your tech startup against Conti type ransomware
Blog written by Alex Jessop, Managing Security Consultant (CIRT) at NCC Group
Background
March saw a 53% increase in ransomware attacks on February, continuing the upward trend for 2022. Conti were the second most prolific group, responsible for 27.52% of the ransomware attacks occurring worldwide[1]. FS-ISAC, in their “Navigating Cyber 2022” report, stated that with the observed trends over recent years, ransomware will remain a top cyber threat to financial institutions[2].
Conti are just another in a long line of Advanced Persistent Threat (APT) actor groups that are targeting organisations for monetary gain. While their arsenal may have some custom tooling, the majority of the Tactics, Techniques and Procedures (TTPs) are well known and used by multiple APT groups. A large proportion of incidents observed by NCC Group would have easily been prevented if policies had been followed or proactive measures taken to understand weaknesses in the environment.
Taking the following three steps will drastically reduce the likelihood of a successful compromise:
- Robust patch management policy
- The majority of initial access vectors observed in Conti attacks would be mitigated
- Enforcing principle of least privilege[3]
- Restricting user permissions would reduce the likelihood of post-exploitation if initial access is gained
- Restricting internet access on servers
- Connectivity is key to threat actors and would make a compromise substantially more difficult if the server estate could not communicate openly with the internet
Executive Summary
In February 2022, a Twitter account which uses the handle ContiLeaks’, started to publicly release information for the operations of the cybercrime group behind Conti ransomware. The leaked data included private conversations between members along with source code methods of delivery. Furthermore, even though the leaks appeared to have a focus on the people behind the Conti operations, the leaked data confirmed (at least to the public domain) that the Conti operators are part of the group, which operates under the TheTrick’ ecosystem. For the past few months, there was a common misconception that Conti was a different entity.
Despite the public disclosure of their arsenal, it appears that Conti operators continue their business as usual by proceeding to compromise networks, exfiltrating data and finally deploying their ransomware. The aim of this article is to describe the methods and techniques we observed during recent incidents that took place after the leaked data.
Our findings can be summarised as below:
- Multiple different initial access vectors have been observed.
- The operator(s) use service accounts of the victim’s Antivirus product in order to laterally move through the estate and deploy the ransomware.
- After getting access, the operator(s) attempted to remove the installed Antivirus product.
- To achieve persistence in the compromised hosts (maintain access), multiple techniques were observed;
- Service created for the execution of Cobalt Strike.
- Multiple legitimate remote access software tools found. These include AnyDesk’, Splashtop’ and Atera’.
- Local admin account Crackenn’ created. (Note: This has been previously reported by Truesec as a Conti behaviour[4])
- Before starting the ransomware activity, the operators are known to have exfiltrated data from the network with the legitimate software Rclone’[5].
It should be noted that the threat actor(s) might use different tools or techniques in some stages of the compromise.
Initial Access
Multiple initial access vectors have been observed recently; phishing emails and the exploitation of Microsoft Exchange servers. The phishing email which was delivered to an employer proceeded to download and install malware which gave the threat actor direct access to the host.
The targeting of Microsoft Exchange saw ProxyShell and ProxyLogon vulnerabilities exploited. This gave threat actors direct access to the Exchange servers. When this vector was observed, the compromise of the Exchange servers often took place two to three months prior to the post exploitation phase.
Other initial access vectors utilised by the Conti operator(s) are:
- Credential brute-force
- Use of publicly available exploits. We have observed the following exploits being used:
- FortiGate VPN
- Log4Shell
- Phishing e-mail sent by a legitimate compromised account, including email accounts of trusted partners
Discovery and Lateral Movement
Once a threat actor has gained access to a host on the network, the threat actor deploys tooling or executes Windows commands to identify hosts on the estate and potential pathways to their objectives.
Typically they begin with network scanning tools to build a picture of the estate and identify what is accessible from the host they currently have access to. Next they will use Windows domain discovery tools to identify users on the domain, as well as user groups which will assist in escalating their privileges .
Lateral movement is usually performed by either:
- Use of Remote Desktop Protocol (RDP) to log onto hosts remotely
- Access across open network shares to copy and execute malware
This phase often occurs within hours or days of initial access being gained.
Persistence
The threat actor leveraged Windows Services to add persistence for the Cobalt Strike beacon. Cobalt Strike is a popular tool for adversary simulation and was the main command and control framework utilised by this group.
In addition, services were also installed to provide persistence for the Remote Access Tools deployed by the threat actor:
- AnyDesk
- Splashtop
- Atera
Local accounts have also been created by the threat actor on patient zero to maintain access.
Privilege Escalation
Conti operator(s) managed to escalate their privileges by compromising and using different accounts that were found in the compromised host. The compromised credentials in engagements undertaken by NCC were found to be compromised through the use of tools such as Mimikatz, which is a well-known tool to extract credentials from running processes.
One operator was also observed exploiting ZeroLogon to obtain credentials and move laterally.
Exfiltration and Encryption
Similar to many other threat actors, Conti operator(s) exfiltrate a large amount of data from the compromised network using the legitimate software Rclone’. Rclone’ is a legitimate file transfer tool which is used to manage files on cloud storage or a private file server. When cloud storage is used, Mega is the option chosen by this group.
Soon after the data exfiltration, the threat actor(s) started the data encryption. In addition, we estimate that the average time between the lateral movement and encryption is five days.
As discussed previously, the average dwell time of a Conti compromise is heavily dependant on the initial access method. Those incidents that have involved ProxyShell and ProxyLogon, the time between initial access and lateral movement has been three to six months. However once lateral movement is conducted, time to completing their objective is a matter of days.
Recommendations
- Monitor firewalls for traffic categorised as filesharing
- Monitor firewalls for anomalous spikes in data leaving the network
- Patch externally facing services immediately
- Monitor installed software for remote access tools
- Restrict RDP and SMB access between hosts
- Implement a Robust Password Policy[6]
- Provide regular security awareness training
References
- https://www.mynewsdesk.com/nccgroup/news/ncc-group-monthly-threat-pulse-march-2022-446743
- https://www.fsisac.com/navigatingcyber2022-report?utm_campaign=2022-GIOReport&utm_source=media&utm_medium=PressRelease
- https://docs.microsoft.com/en-us/windows-server/identity/ad-ds/plan/security-best-practices/implementing-least-privilege-administrative-models
- https://www.truesec.com/hub/blog/proxyshell-qbot-and-conti-ransomware-combined-in-a-series-of-cyber-attacks
- https://research.nccgroup.com/2021/05/27/detecting-rclone-an-effective-tool-for-exfiltration/
- https://www.ncsc.gov.uk/collection/passwords/updating-your-approach
Photo by Tima Miroshnichenko: https://www.pexels.com/photo/people-typing-on-keyboards-5380596/
Payments & Transactions, the fintech opportunity
 is discussing the key outputs in a series of blogs. This blog focuses on Payments & Transactions, which is one of the four key strategic priority themes.
The way we pay for things is changing. Throughout the development of the Research & Innovation Roadmap, payments and transactions were referred to in the broad context of the transfer of value (either money, goods, or assets) in exchange for goods and services.
The Roadmap pinpoints the significant move from physical exchanges to digital transactions, and identifies several significant trends that could mean payments will change significantly in years to come. These changes will have a significant impact on the economy, and could also have a substantial impact on citizens and businesses, which is why the future of payments is one of the four priority themes identified.
The importance of Payments & Transactions
The pandemic accelerated the move from physical to digital in many aspects of our lives, including how we make transactions. Customers’ digital expectations and a shift towards more instant electronic payments are having a significant impact on our economy, and a new digital economy is emerging strongly, with major implications for consumers and SMEs alike.
Across the development of the Roadmap, when looking at the theme of the future payments we considered the topic of digital currencies and crypto currencies. These innovations present new ways for value to be stored and exchanged. It is clear there is a still a lot to learn about the potential, the impact, and the implications of cryptocurrencies as a method for mainstream payments. Stablecoin is a form of cryptocurrency that is linked to an asset that is stable in value, and stablecoins are generating significant interest for future payments and value exchange.
The UK Government has established a crypto assets taskforce, and the UK regulators are considering the benefits and risks on a range of issues connected to this topic, including a separate digital currency backed by a central bank. Since the publication of the Roadmap, HM Treasury has confirmed its commitment to the development of appropriate regulation for crypto.
As we further explored the payments theme, we identified technologies of particular interest, such as AI, blockchain and distributed ledger tools. Industry expressed interest about how these technologies could offer a completely different way to organise and manage payment systems, providing a route to real-time, cross-border payments worldwide. These developments pave the way for a potentially very different future of value exchange. According to the World Economic Forum, up to 10% of global GDP could be stored on blockchains by 2025.
Embedded payments is one of the hottest topics in FinTech in 2022, and was another area of particular focus. Technology is advancing the methods to embed payments in everyday experiences and allow customers and businesses to pay for purchases without entering bank details, credit, or debit card information.
Historically, the payments process has lived at the edges of experience for businesses. Payments were either taken in cash, or offline, with no real lasting insights into the customer and the goods or services they purchased. Technology businesses are now fully embedding software that enables a change to this experience, creating more choice and allowing businesses to have a deeper connection with customers. In addition to high profile examples such as Uber, many embedded payment innovations are emerging, such as in-car payments, smart fridges and connected homes.
Priority areas in Payments & Transactions
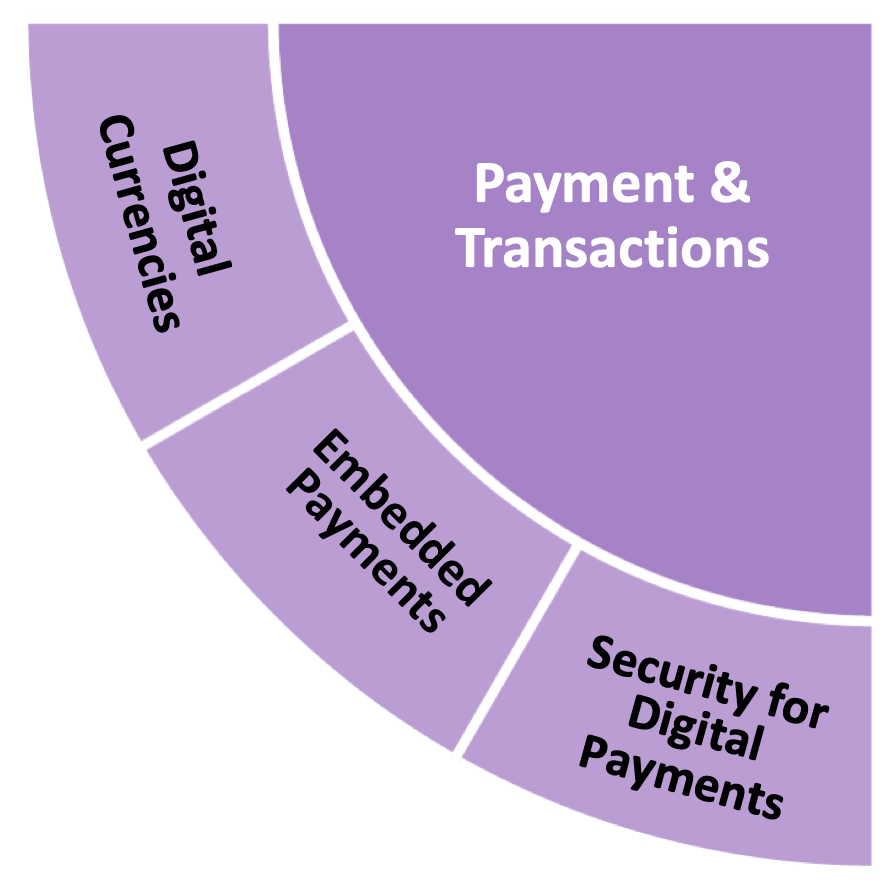
The industry contributors to this roadmap offered a view that the future looks set for significantly more change. Our analysis highlighted three topics of interest:
Digital currencies
- Cryptocurrencies and stablecoins
- Distributed ledger technology
Embedded payments
- SME market
- Retail consumers
Security for digital payments
- Cyber security
- Biometrics
Roadmap next steps: Payments & Transactions
A range of proposed next steps are laid out in the published Roadmap, which specifically identifies 10 actions relating to Payments & Transactions, and categorises each into one of three phases over the next 10 years. These actions are illustrated in the graphic below. The report also references 23 different stakeholders who can support the implementation of these actions, which are broken down into research projects and innovation calls.
More information about FinTech Scotland’s Research & Innovation Roadmap can be found here, where the full Roadmap can also be downloaded.
MyIdentity and Improving Identity Verification
Department for Digital, Culture, Media and Sport (DCMS) and the Digital Identity & Attributes Trust Framework (DIATF)
The Government wants to improve how digital identity is done and demonstrate what a good’ digital identity should look like. As such, the DCMS has made a number of commitments to create a framework for what a good digital identity should look like. They will establish a Governance function to own these rules and make sure that they are followed and develop proposals to remove legislative and regulatory blockers’ for the use of secure identities, whilst ensuring the protection of citizens.
Underneath the DIATF are a number of identity schemes. Each aligned to the DCMS Framework and working to ensure interoperability, as each scheme will have their own nuances to meet the specific needs of its sector.
Etive have been working on the design and development of a scheme for the home buying and selling process since 2018, followed by two rounds of public funding, first from Scottish Enterprise and then Innovate UK.
Is there a problem with identity in the home buying and selling process?
The home buying and selling process is a long transaction built on trust between relying parties – estate agents, conveyancers, brokers and lenders. Each is regulated differently and works to often competing standards and consequently each is not allowed to trust and rely on the identity verification (IDV) carried out by the other.
This has resulted in consumers having to prove their identity up to 5 times through the process, often using different information at different times. This causes great frustration, friction and cost for consumers, as well as relying parties. As one consumer responded, ID checks are currently a joke, I have provided 12 different forms of ID and problems with them all’.
We should also not forget that due to events since 2020, with less face-to-face interactions, there is a greater reliance on digital IDV methods and property and mortgage fraud continues to rise.
MyIdentity Trust Scheme & Regulations
The solution is the development of a trust scheme enabling a consumer to get the IDV done once, which they own, and can share to all relying parties.
The MyIdentity scheme is based on the principles of the DCMS Framework and the Good Practice Guide 45 (GPG45; How to prove and verify someone’s identity). To ensure compliance with Anti-Money Laundering (AML) and compliance for firms, AML regulations were updated in 2019 enabling firms to use an IDV carried out by a certified third party so long as ”¦it is accredited or certified to offer the identity verification service through a governmental or industry process that involved meeting minimum published standards’.
These third parties are identity service providers (IDSPs) and since January 2022 approximately 45 organisations are going the DCMS certification process. Liability has also shifted onto these IDSPs.
Financial Services and MyIdentity
The MyIdentity scheme is participating in the FCA’s regulatory sandbox, enabling firms to test innovative offerings in a live environment and provides FCA regulated firms with the protections that they need to embrace the Government and MyIdentity standards.
MyIdentity is also working through UK Finance to work to get MyIdentity into a position that lenders will accept a MyIdentity IDV and how financial organisations can re-use these IDV’s for all financial services, a re-usable identity, a DCMS objective.
Further work is being done to help remove the blockers for other cohorts involved in the sales process such as conveyancers and brokers who rely on the lender’s handbooks’ from both UK Finance and the Building Societies Association (BSA).
MyIdentity Outcomes
The Beta stage of the project is testing processes and technology looking at improved IDV standards, regulation of providers and greater protections for consumers and the industry.
If we look at Norway, for example, when they developed their trust network, BankID, fraud reduced from 2% of financial transactions to 0.00042% and mortgage lending times reduced to 1 day.
Great work is being done by the industry, coming together, to help improve the process of home buying and selling, also a policy objective of The Department for Levelling Up, Housing and Communities (DLUCH).
FinTech Research & Innovation for Climate Finance
The impact of climate change across the world is disrupting national economies and affecting lives. It requires urgent action from all to address the growing issue.
In its 2020 Global Risks report, the World Economic Forum highlights that the risk signals show the horizon for addressing climate risks has shortened. For the first time in the history of the report, the top five risks that it outlines are in a single category: climate environmental change’
In the Research & Innovation Roadmap, we use the term Climate Finance to describe the role that finance, technology and data can play in addressing the climate change crisis and powering a sustainable future.
The importance of Climate Finance
Enabling a more sustainable future was a prominent theme throughout the research for the development of the Roadmap. Throughout our analysis, the influence of finance together with the potential for exponential change through technologies was thought to be a powerful combination to help the necessary transition to a carbon neutral economy.
In the UK, financial regulators are aiming to influence positive climate outcomes through a series
of new expectations, rules and guidance. The Bank of England is working to encourage an early and orderly transition to a carbon neutral economy and to “play a leading role, through policies and operations, in ensuring the financial system, the macroeconomy, and the Bank are resilient to the risks from climate change and supportive of the transition to a net zero economy.”
The Financial Conduct Authority also has a sustainable finance strategy, aiming to build greater transparency and trust, developing guidance and tools to provide mutual support to address the challenges of climate change.
Climate Finance is a complex matter. Our research with FinTech Scotland showed that it connects many things, including:
- Investment
- Regulatory change
- Better data
- Advanced analytics
- A deeper understanding of consumer behaviours and consumer engagement
- A deeper understanding of new technologies, biodiversity, carbon, and carbon markets
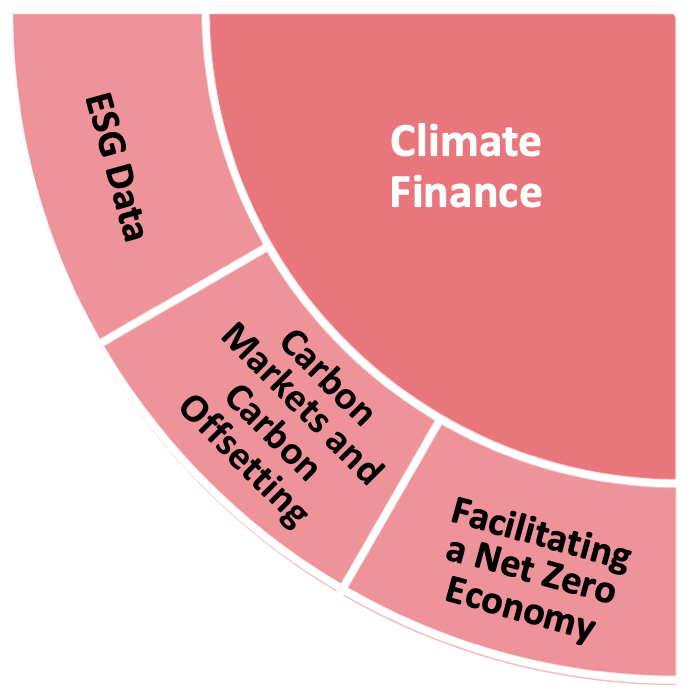
The challenge ahead is huge. Nevertheless, the research behind the Roadmap pinpointed three priority areas where further FinTech research and innovation could advance progress by helping nations adapt to the impact of climate change, manage the risks of transition and lead to them becoming greener, more resilient and more inclusive. All three offer Scotland and the UK an opportunity to use strengths in research and innovation, and to build collaborative action across the FinTech and finance industry and the research community.
Priority areas in Climate Finance
Environment, Social, Corporate Governance (ESG) data.
Assessing the current situation and outlining the ambition for new data sources, clearer standards and advanced analytics to build greater trust and transparency in the sustainable claims made by finance and business.
- ESG reporting
- Investor confidence
- ESG data
- SME market
Carbon markets and carbon offsetting
Considering the role that each plays in realistically transitioning to a net zero low-carbon economy while exploring the technologies and innovation that could drive further progress.
- Voluntary carbon markets
- Carbon offsetting
Facilitating a net zero economy
Moving beyond finance-as-usual practices. Using innovation and technology to reinvent financial markets and stimulate the change needed to support a healthier planet.
- Investment decisions for net zero
- Circular economy
- Housing
- Insurance
- SME market
Roadmap next steps: Climate Finance
A range of proposed next steps are laid out in the published Roadmap, which specifically identifies 8 actions relating to Climate Finance, and categorises each into one of three phases over the next 10 years. These actions are illustrated in the graphic below. the report also references 25 different stakeholders who can support the implementation of these actions, which are broken down into research projects and innovation calls.
More information about FinTech Scotland’s Research & Innovation Roadmap can be found here, where the full Roadmap can also be downloaded.
Research & Innovation opportunity in Open Finance data
Article written by Julian Wells, Director at Whitecap Consulting
FinTech Scotland recently published its 10 year Research & Innovation Roadmap. Whitecap worked in partnership with the FinTech Scotland team to support the development of this roadmap, and is discussing the key outputs in a series of blogs. This blog focuses on Open Finance data, which is one of the four key strategic priority themes.
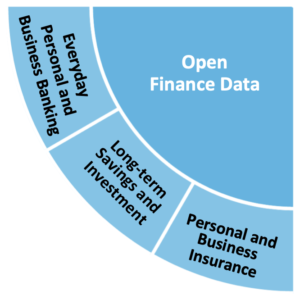
In the first blog in this series, we discussed the purpose, value and impact of a Research & Innovation Roadmap. In this blog, we discuss Open Finance data which is a strategic priority itself but also a facilitator of FinTech innovation in wider areas, and an enabler for the three other strategic priority themes in the Roadmap.
The other three themes are Climate Finance, Payments & Transactions, and Financial Regulation, each of which will be the subject of a subsequent blog in this series.
Open Finance data has the potential to significantly change consumers’ and businesses’ engagement with finance, and to deliver better outcomes. It spans the whole suite of financial products and services as we understand them today, including banking, savings, mortgages, pensions, investments, insurance, lending, and payments.
How can Research & Innovation support the development of Open Finance?
To help Open Finance achieve its potential, more leadership, actionable research, and innovation is required. FinTech Scotland’s Research & Innovation Roadmap sets out specific actions to help drive this opportunity ”“ through a collective approach that involves industry, innovators and researchers ”“ to create the future of finance.
Open Finance can create progressive change that will move the UK forward significantly, by moving beyond banking and asking other financial institutions (such as pension providers, asset managers and insurers) to enable customers to share their data with others.
This would open up a wider range of financial products and services to the transformative impact of third-party innovation through trusted data sharing. For consumers and businesses, it offers new ways to understand their finances, receive financial advice, and compare financial product features and prices.
Research and innovation are needed to facilitate the potential of Open Finance data, building economic growth and creating employment opportunities in high value sectors which in turn will make the UK an attractive destination for inward investment.
Furthermore, it will help us better understand, measure, and forecast the considerable impact that Open Finance could have on society and to shape future policy.
In the UK, one of the key enablers of research and innovation in Open Finance is the Smart Data Foundry (formerly The Global Open Finance Centre of Excellence), which has been established in Edinburgh to support the understanding and development of the capabilities of Open Finance. It has a leadership role in enabling the necessary research and innovation, and building confidence in Open Finance across the UK, and can encourage research and innovation by providing a highly secure environment that can host Open Finance data. The Open Finance data priority in FinTech Scotland’s Research & Innovation Roadmap supports and complements The Smart Data Foundry’s agenda.
Priority areas in Open Finance data
When developing the Roadmap, analysis highlighted three industry priorities that will benefit from more focused research and innovation on this topic. They involve shaping the future of:
Everyday personal banking and business banking
- Insights through Open Banking data
- Future banking business models
Long-term savings and investment
- Financial resilience and wellbeing
- Future living & the ageing population
Personal and business insurance
- New data and insights for insurance
- Data privacy
- Data ethics and governance
Roadmap next steps: Open Finance data
A range of proposed next steps are laid out in the published report, which specifically identifies 22 actions relating to Open Finance, and categorises each into one of three phases over the next 10 years. These actions are illustrated in the graphic below. the report also references 23 different stakeholders who can support the implementation of these actions, which are broken down into research projects and innovation calls.
Why should tech companies care about double fetch vulnerabilities?
Fintech companies are facing an increasing need to focus on cybersecurity. Whilst cyber-attacks are on the rise and necessitate the constant evolution of cyber-security solutions, very often the issues arise from known vulnerabilities within existing systems.
In this blog we’re exploring double fetch vulnerabilities.
The phrase ‘double fetch bug’ was first used by Fermin J. Serna in a post on the Microsoft Security and Defense Blog in October 2008, although the bug type had been known about for some time before this.
Double fetch vulnerabilities in C and C++ have been known about for a number of years. However, they can appear in multiple forms and can have varying outcomes.
As much of this information is spread across various sources, the whitepaper, draws the knowledge together into a single place, in order to better describe the different types of the vulnerability, how each type occurs, and the appropriate fixes.
There are two broad general types of double fetch vulnerability: those resulting from coding practices and those introduced by compiler optimization, referred to as a ‘compiler introduced double fetch’ below and in the whitepaper.
The two types of double fetch bug both have the same result, whereby an invariant exists involving two or more variables and one or more of these variables is modified without the invariant being enforced.
Since double fetch bugs can have varying causes, we must consider different solutions for the two different subtypes of double fetch.
- Double fetch bugs caused from accessing shared memory may be fixed by adding a check against the second fetch, eliminating the second fetch (where practical), or performing the check in a different manner.
- For compiler-introduced double fetches, the use of volatile variables is one possible solution to the double fetch problem.
In conclusion, double fetch bugs can result in privilege escalation vulnerabilities that can allow an attacker with a low privilege account to execute code with elevated privileges, although the exploitable vulnerabilities are a relatively small subset of these bugs.
To understand how to best protect yourself against these vulnerabilities, click here to access the full whitepaper from NCC.
Why is the FinTech Research & Innovation Roadmap so important?
Article written by Julian Wells, Director at Whitecap Consulting
FinTech Scotland, the cluster management body, recently published its 10 year Research & Innovation Roadmap. Whitecap worked in partnership with the FinTech Scotland team to support the development of this roadmap, and in the first in a series of blogs we discuss the fundamentals behind this important document.
FinTech is driving change in one of the most important parts of our economy. It presents a significant disruptive force in financial services, and will shape the future of the digital economy. It has the potential to radically change the way people and businesses engage with money, and to create a new financial system that is more effective and resilient.
FinTech Scotland’s Research & Innovation Roadmap is a 10 year plan which has been developed as an industry-led and action-focused tool to increase the positive impact of FinTech innovation across Scotland and the UK. It creates a framework and an environment to drive greater collaboration, and to build the connections that will enable responsible innovation for the future of finance.
The roadmap builds on foundations that were already established through the FinTech Scotland cluster, and sets out the cross-sectoral strategic priorities that ”“ through collective and collaborative action ”“ will shape the future of financial services, and enable Scotland and the UK to further advance FinTech innovation. It was published on the anniversary of the HM Treasury commissioned Review of Fintech led by Ron Kalifa OBE which set out a number of recommendations, including the opportunity for research and innovation to accelerate the development of cluster excellence.
Why do we need a Research & Innovation Roadmap for FinTech?
The financial services industry contributes £132 billion to the UK economy ”“ almost 7% of total economic output. It is an essential part of the full UK economy that enables prosperous outcomes for businesses and people across the UK. Its significance was highlighted by the Chancellor of the Exchequer in the recent HM Treasury report A new chapter for Financial Services’. Working with others across the economy, his vision is for “an agile and dynamic approach, one which enables those in the financial services industry to evolve and thrive as they embrace the new opportunities of the future.”
Research and innovation play a key role in the vision for the future of financial services in the UK and beyond. However, financial services and FinTech have, compared to other industries, generally not been aligned with the academic research communities. Recent analysis highlighted that research funding into these fields is as low as 3% of total UK funding1 for research and innovation.
In addition, there is a general acknowledgement in financial services, FinTech, and the academic community that current engagement has had a relatively narrow focus. The result is limited exploration of research and innovation, which means an important part of the economy is not fulfilling its full potential.
There is an opportunity to close the gap between the economic productivity of UK financial services and the current scale of UKRI investment in FinTech and financial services R&I. This can be achieved via more strategic and systematic collaboration, which can help develop the necessary FinTech innovation between the range of stakeholders. Importantly, this should be driven by a true desire for effective change, and by an industry-first real-world’ approach to the challenges ahead.
This work also supports the strategic HM Treasury Review of UK Fintech led by Ron Kalifa OBE. It recognises the value of collaboration, and the leadership that is needed to create the right conditions for FinTech to innovate, accelerate and grow.
How will the Roadmap be implemented?
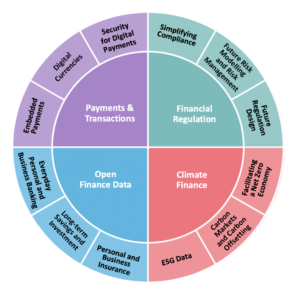
The priority themes form the building blocks of the Roadmap are: Open Finance data, Climate Finance, Payments and transactions, and Financial regulation. In subsequent blogs in this series we will focus on each of these four themes individually.
The roadmap will be led and facilitated by FinTech Scotland. However, wider stakeholder participation is required to implement the R&I actions set out in this Roadmap.
Actions will be progressed through two key types of activity:
Unleashing Innovation: A series of Open Innovation Calls, using technologies and data to develop new and improved financial products and models.
A rollout plan will be developed to implement a programme of innovation calls. This will include developing a sponsorship proposition to maintain the commitment for an industry-led programme.
The initial steps for the Roadmap innovation calls include:
- Work with the Smart Data Foundry to start the implementation of the priority innovation calls identified in the Roadmap.
- Continue the work with industry stakeholders to refine a series of problem statements for each theme, ensuring industry value in the future solutions.
- Market the innovation calls across UK and international FinTech clusters, raising the profile of FinTech innovation in Scotland.
Actionable Research: Research, using technologies and data to create actionable insights that can be applied commercially using FinTech.
FinTech Scotland will engage with academic community in respect of the research topics proposed. FinTech Scotland will also engage with research funding organisations such as UKRI / Innovate UK to ensure this roadmap is fed into future funding calls.
The initial steps for research topic actions include:
- Work with university leaders to generate research briefs that directly respond to the actions identified in the roadmap.
- Establish relevant steering groups demonstrating collaboration across industry and the research community.
- Monitor and review progression (including a KPI scorecard).
Twice a year, the FinTech Scotland Cluster Management Board will measure and review the Roadmap’s progress of the Roadmap. This will be reported publicly to stakeholders in Scotland and the UK.
What will the impact of the Roadmap be?
In this blog we have outlined the requirement and benefits to bringing industry-led approach to research and innovation, but describing the impact the Roadmap can have on the Scottish and UK economy is perhaps the most compelling way to explain why this is such a vital document.
The overarching economic ambition for the Roadmap is to do two things:
- Create up to 30,000 extra jobs in Scotland.
- Increase economic value (GVA) by more than 330% ”“ from £598 million to more than £2 billion ”“ over ten years.
Taking a broader perspective, the impact of the Roadmap will be:
- To tangibly help improve lives for citizens, by tackling inclusion and health- related issues.
- To further develop Scotland as part of the UK in being a global engine room’ for FinTech and a desirable location for international FinTech companies.
- To drive innovation, supported by a world-leading reputation in regulation and compliance.
- To use Scotland’s and the UK’s natural strengths, making them a global enabler of greener’ FinTech.
A blueprint for the future
FinTech Scotland’s Research & Innovation Roadmap outlines actionable research and innovation activities that can help develop economic, environmental, and societal value for Scotland and the UK through FinTech. Successful implementation will require the engagement and co-operation of key stakeholders within the FinTech Scotland cluster, and stakeholders from across the UK and internationally. The Roadmap is the first of its kind in the UK, but the aspiration is that it has created a framework that other countries, regions or indeed FinTech sectors can learn from and adapt.
More information about FinTech Scotland’s Research & Innovation Roadmap can be found here, where the full Roadmap can also be downloaded.
FinTech research and Innovation ”“ the future of finance
This month we published our FinTech Research and Innovation Roadmap. We know more research and innovation in financial services and fintech will set us on a course to shape the future of finance.
It’s been in the works over recent months, and it’s allowed us an opportunity to hear industry, consumer academic, and innovators views on what the future of finance and fintech could be. Leading the way!
It’s a genuine privilege to hear the ambition and determination across the fintech and finance industry for a future that means less friction in financial services, enables more inclusion using technology and data, and drives climate change enabling greener investments.
The tone from all was clear, fintech will drive better financial outcomes for people, businesses, our society, and the environment. The desire for change and energy for innovation and collaboration is truly inspiring.
The report gives us a framework for focused collaboration. It identifies 4 priority themes and outlines the primary actions that will enable us all to learn, advance, and most importantly, build the right collaborations to drive and lead future fintech innovation. It was published during the first anniversary of the Kalifa review of UK Fintech where more R&D was a specific recommendation.
The first of those priority themes in Open Finance Data ”“ already an area of strength in Scotland! FinTech businesses such as DirectID, Visible Capital, Inbest, AirFunders, and One Bank all use Open Finance Data in their businesses. This experience along with the investment in the Global Open Finance Centre of Excellence, now known as the Smart Data Foundry sets us on a course to explore how Open Finance Data can change the way we do finance in the UK and across the world.
Climate Finance is another key priority ”“ a growing area of strength and focus for Scotland. FinTech businesses such as Snugg, Coastr, Pulse, Iceni Earth, Trade in Space, and Space Intelligence are all focused on using data and technology to help people and businesses make the changes needed to achieve change in the interests of the planet. These businesses are enabling a different future. The same can be said for the research community in Scotland with centres such as The Centre for Sustainable Developmentand the Edinburgh Climate Change Institute leading research and providing deeper and focused insights on climate impact. From this place of understanding more will change.
Payments and transactions’, as well as Financial Regulation’ complete the 4 priority themes. Again, both assets for Scotland, where the depth of fintech innovation, skills and expertise stand Scotland’s FinTech Cluster in great stead. More on both these themes in the coming weeks and months.
For now, we’re gearing up for UK FinTech next week. There’s a host of events in plan where we’ll have an opportunity to share the wonderful work happening across FinTech Scotland.
I’m signing off with a note of thanks and a special note of thanks to everyone who contributed to the FinTech Research and Innovation Roadmap.
The Roadmap is a true demonstration of Scotland’s FinTech Cluster at its best. It highlights the breadth of contribution to the cluster that allows us to learn, collaborate and inspire each other for development and growth. It shows how our commitment to action for positive change, and it is ambitious, challenging us to think ten years ahead so we can lead the future of finance.
I’m looking forward to seeing this advance and working with the inspiring leaders, innovators, entrepreneurs, and educators as we build and teach the future!
Thank you
Nicola